Website Spam Is More Than an Annoyance. It’s a Business Problem.
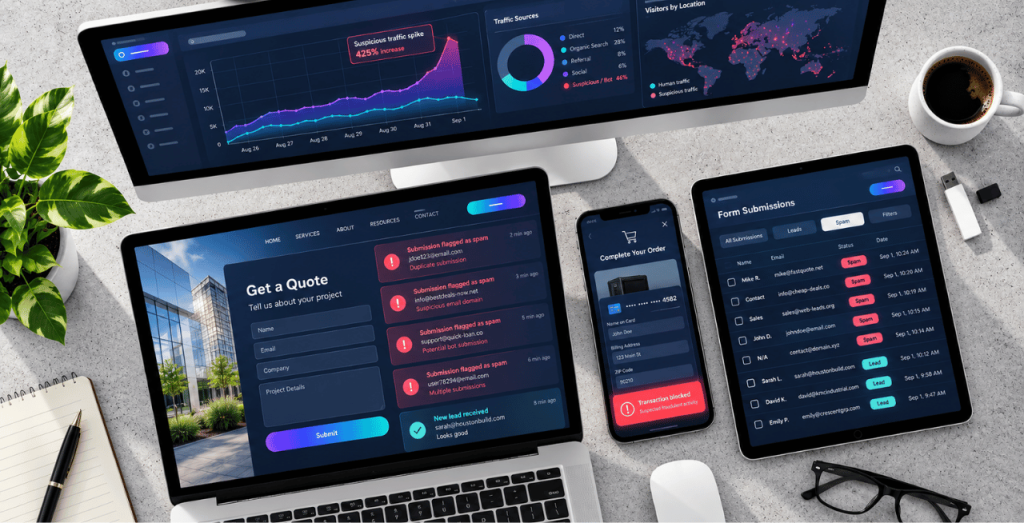
If you run a website, you’ve probably dealt with spam in some form. Maybe your contact form floods your inbox with gibberish. Maybe your blog comments fill up with links to sites you’d never endorse. Or maybe you’ve seen something worse: dozens of small, failed credit card transactions hitting your online store overnight.
Spam used to be a nuisance. Today it’s often automated, AI-assisted, and aimed squarely at your revenue, your reputation, and your marketing budget.
At Apache Interactive, we’ve recently worked with several clients, especially those with e-commerce websites, who were hit hard by bot traffic. This article covers the main types of spam, why they’re so frustrating, and the steps we’ve used to fight them.
The Most Common Types of Website Spam
1. Form Spam
Any form on your website can become a target: contact forms, quote requests, newsletter signups, comment sections, and account registrations. Bots fill them out automatically, sometimes with junk, sometimes with links to malicious sites, and sometimes just to probe for weaknesses.
Why it hurts:
- Real leads get buried under fake ones
- Your team wastes time sorting through junk
- Your CRM and email lists fill up with bad data
- Your email deliverability can suffer if fake addresses bounce
2. E-Commerce Card Testing and Fake Orders
This is one of the most damaging types. In a “card testing” attack, criminals use bots to run stolen credit card numbers through your checkout to see which ones work. They typically make small purchases or attempt low-dollar transactions, and they do it at high volume.
Why it hurts:
- You may pay gateway fees on every attempt, even the failed ones
- Chargebacks and disputes can follow
- Your payment processor may flag or even suspend your account
- Your order data, reports, and inventory get polluted
- It feels like online harassment, because it is
3. Ad Click Fraud
If your Google Ads campaigns run on the Display or Search Partner networks, your ads can appear on many third-party websites. Some of those sites are operated by people who profit when ads are clicked, so they use bots to click them. In other cases, a competitor may try to drain your budget.
Why it hurts:
- Your ad budget is spent on clicks that will never convert
- Your data looks worse than it really is, leading to poor decisions
- Your cost per lead climbs while lead quality drops
4. General Bot Traffic
Scrapers, vulnerability scanners, and fake visitors inflate your analytics, slow your site, and add to hosting load. This can distort the metrics you rely on to judge whether your marketing is working.
Why This Fight Keeps Getting Harder
Spammers now use AI tools to build smarter bots. Modern bots can mimic human behavior, vary their messages, and slip past older defenses that once worked well.
There is no single “set it and forget it” fix. The best approach is layered protection: several defenses working together, reviewed and updated regularly.
Step 1: Protect Your Forms
At a minimum, every form on your site should be protected by a modern bot-detection tool.
Cloudflare Turnstile (our preferred option). Turnstile is a CAPTCHA alternative that verifies visitors are human without making them click traffic lights or decode blurry letters. That means less friction for real customers and better protection against bots. It’s free, easy to integrate with WordPress forms, and privacy-friendly.
Google reCAPTCHA. This is still a solid option and far better than no protection at all. If your site already uses it, keep it in place until you can evaluate a switch.
Additional form defenses worth considering:
- Honeypot fields: hidden fields that real users never see but bots fill out automatically
- Spam filtering for comments: tools like Akismet catch a large share of comment spam
- Rate limiting: restricting how many submissions can come from one source in a short time
- Double opt-in for email signups: confirming the address before adding it to your list
- Turning off comments on pages and posts where they add no value
Step 2: Run Your DNS Through Cloudflare
Routing your website’s DNS through Cloudflare puts a protective layer between the internet and your site. Bad traffic can be filtered before it ever reaches your server. A few of the features we find most useful:
- Bot protection: Cloudflare can identify and challenge suspicious automated traffic
- Web Application Firewall (WAF) rules: custom rules that block or challenge requests based on behavior, IP reputation, and other signals
- Rate limiting: limits how often a visitor can hit a login page, checkout, or form
- Managed challenges: suspicious visitors are asked to prove they’re human, while normal visitors pass through untouched
- Country and region rules: block or challenge traffic from places you don’t do business with
- DDoS mitigation: helps absorb floods of malicious traffic
A Note on Geo-Blocking
If you’re a local business, you may have no reason to accept traffic from other countries. A Houston plumbing company probably doesn’t need visitors from overseas. Cloudflare makes it easy to restrict or challenge traffic by country.
But it isn’t foolproof. Determined spammers can use VPNs, proxies, and other tools to appear as though they’re coming from an allowed location. Think of geo-blocking as one helpful layer that reduces noise, not a complete solution.
Step 3: Stop Fraud Before It Reaches Your Payment Gateway
For e-commerce sites, prevention has to happen before the transaction is sent for processing, because that’s when fees and processor scrutiny begin.
Fraud scoring with FraudLabs Pro. We’ve had great success with FraudLabs Pro. It evaluates each order attempt using multiple signals, including the customer’s email address, IP address, and other risk factors, and assigns a fraud score. Suspicious orders can be blocked before they ever reach your payment gateway.
What that prevents:
- Extra gateway fees on junk transactions
- Chargebacks and disputes
- A flood of fraud-related notification emails
- Warnings from your payment processor
Email verification before checkout. In some cases, we’ve added a step where customers must verify their email address before they can complete a purchase. Bots and fraudsters often use throwaway or fake addresses, so this simple step stops a large share of them.
Business-email-only requirements (for B2B sites). If your customers are other businesses, you can require a business email address and block free, commonly abused providers. This filters out casual fraud and low-quality submissions. Just be sure it fits your audience. It’s a great fit for many B2B and industrial sites, but not for consumer stores.
Other e-commerce safeguards to consider:
- Require CAPTCHA or Turnstile at checkout and on account registration
- Limit repeated failed payment attempts from the same IP or session
- Use address and security code verification (AVS and CVV) checks through your gateway
- Turn on the fraud tools built into your processor
- Monitor your transaction logs for bursts of small, failed payments, a classic sign of card testing
- Set alerts so you hear about unusual activity quickly, not weeks later
Step 4: Defend Your Ad Budget Against Click Fraud
If you’re investing in paid advertising, click fraud protection can be one of the highest-return investments you make.
ClickCease is one of our favorite tools for this. Like FraudLabs Pro, it evaluates visitors, identifies suspicious IP addresses and behavior patterns, and blocks them from seeing or clicking your ads in the first place.
Depending on your budget and industry, that can mean saving thousands of dollars in wasted ad spend.
Additional ways to reduce ad waste:
- Review your Google Ads placement reports and exclude low-quality sites
- Consider opting out of the Display Network and Search Partners if they aren’t performing
- Watch for click spikes that don’t produce engagement or conversions
- Compare ad clicks to actual site sessions and engagement time
- Use IP exclusions for repeat offenders
Step 5: Clean Up Your Analytics
Even with strong defenses, some bot traffic will slip through. Regularly review your analytics for warning signs such as:
- Sudden traffic spikes from unexpected locations
- Very short session times or 100% bounce rates from one source
- Strange referral sources
- Form submissions with no matching visitor engagement
Filtering out known bot traffic and internal traffic helps you make decisions based on real human behavior, not inflated numbers.
The Goal: Real Traffic From Real Humans
Spam prevention isn’t only about avoiding annoyance. It’s about making sure the visitors, leads, and customers you’re paying to attract are real. When bots are removed:
- Your lead data becomes trustworthy
- Your ad spend goes further
- Your team focuses on real prospects
- Your analytics reflect what’s actually happening
- Your site is faster and safer
That means real people who stay longer, engage with your content, and buy from your business.
Quick Website Spam Prevention Checklist
- Turnstile or reCAPTCHA on every form
- Honeypot fields and spam filtering on forms and comments
- DNS running through Cloudflare with WAF and bot protection enabled
- Rate limiting on login, checkout, and forms
- Geo-restrictions for local businesses (with the understanding they aren’t foolproof)
- Fraud scoring on e-commerce checkout
- Email verification (and business-email requirements where appropriate)
- Click fraud protection on paid ad campaigns
- Analytics filtered and monitored regularly
- Someone assigned to review and update these defenses regularly
Fighting Spam Is an Ongoing Battle. You Don’t Have to Fight It Alone.
Spammers keep evolving, and so do we. Our team continually studies new attack methods and adapts our defenses so our clients get real traffic, real leads, and real sales.
If you’re dealing with form spam, fake orders, wasted ad spend, or suspicious traffic, we’d like to help. Contact Apache Interactive to talk with our team about a plan to protect your website and your marketing investment.
Let's Do This Together.
Join over 10,000 subscribers that receive our digital newsletter, full of actionable news and information you can apply to your business. Sign up today!
Sharing Is Caring.
Share this post with all of your contacts by using the social sharing links below.
Related Content.
To Go Fast, Go Alone. To Go Far, Go Together.
Are Your Ready To Take The Next Step? Drop us a line today for a free consultation.
Get In Touch
Apache Interactive
Kingwood Texas
832.971.4905
[email protected]
We Love Referrals
Privacy and Security
Who We Are And What We Do
Apache Interactive is a digital marketing agency specializing in technical SEO, online advertising (PPC), content marketing, and web design and development services.
We work directly with client companies, and also partner with other marketing and branding agencies that want to have a digital marketing expert on call to assist with challenging projects.

Stay Connected
The Internet is a big place and we love to hang out on all of the major social networks.
Follow our accounts and never miss any of our photos, videos, or other digital marketing mayhem.